Installing Factry Historian for production use
This guide will help you install Factry Historian with standard settings for a production-ready installation. It is written for technical users who are comfortable working with a terminal and know basic networking concepts.
At the end of this guide, you will find additional steps to configure TLS certificates, external authentication providers, proxy servers, and other settings.
During this guide, you will have to configure users, passwords and secrets. We recommend storing these secrets securely, for example in your password manager.
Prerequisites
Before you start, make sure you have the following in place:
- License
- Infrastructure
- System Resources
- Networking
License
To download Factry Historian and install it for production use, make sure you have obtained a license key and signed a license agreement with Factry. If you have not done so already, please contact Factry to obtain a license.
Once both are in place, Factry will provide you with access to the Factry Historian portal. On the portal, you will be able to download all binaries needed for this guide.
Infrastructure
- A supported version of Ubuntu server LTS (Download latest Ubuntu LTS image)
- Terminal access with administrative privileges
System Resources
Load | Writes / second | Queries / second |
|---|---|---|
Low | < 5.000 | < 5 |
Moderate | < 100.000 | < 25 |
High | >= 100.000 | >= 25 |
Low
- CPU: 4 cores
- Memory: 8 GB RAM
- Database disk: >= 500 IOPS
Moderate
- CPU: 8 cores
- Memory: 16 GB RAM
- Database disk: >= 1.000 IOPS
High
High loads should be tested before being deployed to production:
- CPU: 16 cores
- Memory: 64 GB RAM
- Database disk: >= 1.000 IOPS
Required disk space starts at 100GB and should be expanded based on expected write load.
Networking
To install and access the services using this guide:
- Internet access to download Factry Historian and prerequisities
- A fixed (local) IP adress for the server
For a standard setup, the following ports should be available before starting the setup:
- Factry Historian: TCP port 8000 (HTTP) and 8001 (gRPC)
- Grafana: TCP port 3000
Install Dependencies
1. Update package list and download wget
sudo apt-get update && sudo apt-get install wget2. PostgreSQL
Install PostgreSQL
sudo apt-get install -y postgresql postgresql-contribVerify if PostgreSQL is running
sudo systemctl status postgresql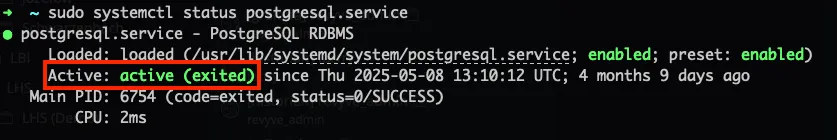
Create PostgreSQL superuser
- Replace <username> with your desired username (e.g. factry)
- You will be prompted to enter and confirm the password for the PostgreSQL superuser.
sudo -u postgres createuser -s <username> -PCreate Grafana database and administrator user
Open the PostgreSQL CLI:
sudo -u postgres psqlThen perform the following commands. Replace <'password'> with your desired password (e.g. 'my-password', keep the surrounding '). Replace <username> with your desired username (e.g. factry).
CREATE USER grafana WITH ENCRYPTED PASSWORD <'password'>;
CREATE DATABASE factry_historian OWNER <username>;
CREATE DATABASE grafana OWNER grafana;
exit
The first line creates the grafana user. The second line creates the database factry_historian with the given username as the owner. The third line creates the database grafana with the grafana user as the owner. The fourth line exits the postgreSQL CLI.
3. InfluxDB
Download and install InfluxDB
The first line downloads and installs the InfluxDB (v1.12.x) database which stores the time-series data points and logs collected via Factry Historian.
cd /tmp
wget https://dl.influxdata.com/influxdb/releases/v1.12.4/influxdb_1.12.4-1_amd64.deb
sudo apt-get install -y ./influxdb_1.12.4-1_amd64.deb
sudo systemctl enable --now influxdb
Verify if InfluxDB is running
sudo systemctl status influxdbCreate InfluxDB users
Open the InfluxDB client CLI.
influxCreate a user with administrative privileges in InfluxDB.
- Replace <admin_username> with your desired administrator username (e.g. factry) and replace <password> with your desired password (keep the ' around the password).
- You will be prompted to enter and confirm the password.
CREATE USER <admin_username> WITH PASSWORD '<password>' WITH ALL PRIVILEGES;Shows the users available in InfluxDB, check if the admin user is created.
SHOW USERS;Exit the InfluxDB CLI.
exitConfigure InfluxDB
Open your text editor of choice and make the following changes:
sudo vi /etc/influxdb/influxdb.confIn the [data] section:
- edit query-log-enabled to false to disable (an abundance of) queries being captured in the logs.
In the [http] section:
- edit auth-enabled to true to enable authentication on InfluxDB.
- edit log-enabled to false to disable (an abundance of) API queries being captured in the logs.
Make sure to remove the # before the indicated lines for them to be picked up as configuration and not as a comment.
[data]
query-log-enabled = false

[http]
auth-enabled = true
log-enabled = false
After making changes, restart InfluxDB for the changes to take effect
sudo systemctl restart influxdb4. Grafana
Download and install Grafana
Download the latest supported version of Grafana, by following their guide. E.g. for version 12.1.1, use the following commands:
sudo apt-get install -y adduser libfontconfig1 musl
wget https://dl.grafana.com/grafana/release/12.1.1/grafana_12.1.1_16903967602_linux_amd64.deb
sudo dpkg -i grafana_12.1.1_16903967602_linux_amd64.deb
sudo systemctl enable --now grafana-server
Configure Grafana
Open your text editor of choice and make the following changes:
sudo vi /etc/grafana/grafana.iniIn the [database] section:
- edit type to postgres to setup the Grafana internal database with PostgreSQL
- set hostto localhost:5432(or the host:ip of your PostgreSQL database)
- set name to grafana to set the database name
- set user to grafana to set the user to connect (user created in 2.PostgreSQL )
- set password to the password of that user (Replace <my-password> with the password and keep the surrounding """ to allow special characters)
- set ssl_mode to disable to successfully connect with the PostgreSQL database over localhost
Make sure to remove the ; before the indicated lines for them to be picked up as configuration and not as a comment.
[database]
type = postgres
host = localhost:5432
name = grafana
user = grafana
password = """<my-password>"""
ssl_mode = disable
After making changes, restart Grafana for the changes to take effect
sudo systemctl restart grafana-serverVerify if Grafana is running
sudo systemctl status grafana-serverInstall Factry Historian datasource in Grafana
Install the Factry Historian datasource plugin in Grafana to easily fetch Historian data in Grafana, and restart Grafana for the changes to take effect.
sudo -u grafana grafana-cli plugins install factry-historian-datasource
sudo systemctl restart grafana-server
5. Lock dependency versions (Optional)
Lock the versions of the installed services to prevent unintentional updates to the installed services when (automated) patches are performed on the server.
sudo apt-mark hold postgresql influxdb grafana6. Install Factry Historian
Login to the Factry Historian Portal and download the Factry Historian installation executable for your CPU architecture.
- Navigate to https://portal.factry.cloud
- Login with your credentials
- Once logged in, click Downloads in the header menu
- In the Downloads panel:
- Select a release channel (Stable)
- Select a product (Factry Historian)
- Select a version
- Select an OS/Platform (Linux/AMD64)
- For an offline installation, click Download to download the binary and manually copy it to the host system. For installation on a system with internet access, click Copy URI to copy the link and download it with e.g. wget.
- Place to executable on a location where you have write access e.g. your home folder.
Replace the factry-historian-server_vx.x.x filename with the filename of your executable. Perform the command(s) in the CLI:
chmod a+x factry-historian-server_vx.x.x
sudo ./factry-historian-server_vx.x.x install
Verify if Factry Historian is running
sudo systemctl status factry-historian-serverFor more options and details, follow Downloading and Installing Factry Historian server.
7. Synchronize server time with NTP (Recommended)
Show the time and date on the server and the state of NTP synchronization.
timedatectl- Check if the time and date are set correctly. Note that the timezone is typically set in UTC: Compare time between different timezones.
- Check if NTP service states active, which indicates that the server is synchronized with an NTP server.
Is the date and time not correct or the NTP service is not active? See the Troubleshooting section.
8. Confirm service availability
Verify if you can access Factry Historian and Grafana in the browser:
- Historian: http://xx.xx.xx.xx:8000
- Grafana: http://xx.xx.xx.xx:3000
If that is not the case, see the Troubleshooting section.
Make sure to use http:// in your browser. Some browsers override it automatically to https://, in which case use an incognito window.
🎉 Congratulations! You have successfully installed Factry Historian and Grafana.
Next steps
Security
For additional security, we recommend the following additional steps:
- Add HTTPS: reverse proxy Factry Historian and Grafana, then install the certificates on the proxy webserver.
- Configure external Authentication Providers
Configuration
- Further configure Factry Historian according to your preferences. Consult the Reference documentationReference documentation.
Data collection
Troubleshooting
Services: See logs
These lines show the service logs of the according service unit with -u, and with -rsorted in reversed time order (newest logs on top).
journalctl -u postgresql -r
journalctl -u influxdb -r
journalctl -u grafana-server -r
journalctl -u factry-historian-server -r
Services: Verify if port is accessible
Check if the server is accepting TCP connections (replace xx.xx.xx.xx with your Factry Historian Ubuntu server IP address) on the appropriate port. For example, with telnet:
telnet xx.xx.xx.xx 8000If successful, the output states Connected to .... Press CTRL + ] and CTRL + C to exit the command.
NTP synchronization for correct date and time
Open the NTP synchronization settings using your editor of choice:
vi /etc/systemd/timesyncd.confChange the configuration to point to public NTP servers, or configure your company's NTP servers.
An example with Ubuntu's NTP servers:
Save the file and exit your editor.
Restarts the timesyncd service for the changes to take effect. Next, enables NTP synchronization. Then check if the status of the timesync service is set to Active.
systemctl restart systemd-timesyncd
timedatectl set-ntp true
systemctl status systemd-timesyncd
Need help?
Contact Factry for licenses, support, or migrating from legacy historians.